Risks
Map your exposure
Link risks, assets and processes; set treatment priorities.
AI & Cybersecurity
Managed Services
Governance, Risk, and Compliance
Offensive Security
Security Assessment
Strategic Advisory
Training & Awareness
Internship Positions
Junior Positions
Connect your risks, your obligations and your evidence. Give your teams a shared view to make decisions.
From asset to requirement, a chain of control that makes responsibilities and decisions visible.
Risks
Link risks, assets and processes; set treatment priorities.
Actions
Assign an owner and track measures, deadlines and progress.
Compliance
Organize frameworks, assessment campaigns and identified gaps.
Evidence
Attach documents, tests and versions to the requirements you must demonstrate.
Features depend on configuration and access rights; scope validated during the pilot. Illustrative visuals.
Assets
Business processes
Risks
Criticality and plans
Controls
Measures and tests
Evidence
Documents and audit
A structured path for business teams, risk managers and auditors.
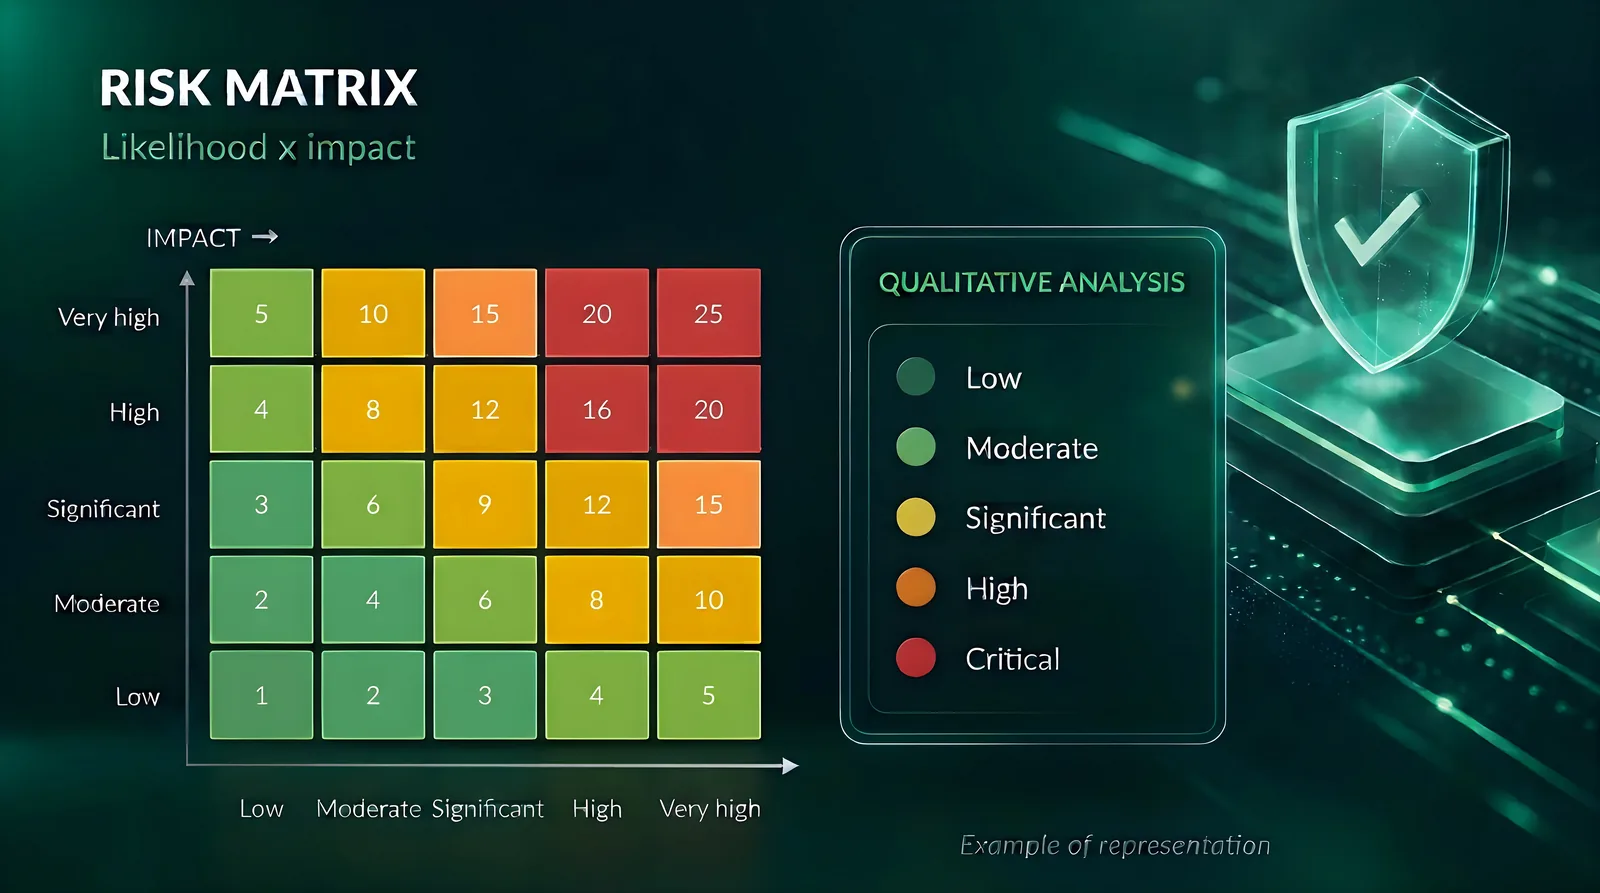
Shared reading
Compare risks and identify those to treat first.
Decision tracking
Link actions to owners and deadlines.
Illustrative risk matrix, not based on customer data. Methods are qualified during the pilot.
One vision.Clear priorities.Solid evidence.
Govern / Assess / Demonstrate
Qualify your risk management method and frameworks on a real scope before extending it.
Scoping
Define assets, processes, roles and frameworks.
GRC pilot
Test campaigns, controls, evidence and actions.
Qualification
Validate reporting, access and operations.
Option: local AI assistance in beta, under human validation.

A first pilot adapted to your context
Let's build a representative, measurable pilot together.